ISSA South Texas Chapter Meeting - Agentic GRC - October 8, 2026

About this Event
ISSA South Texas Chapter meeting and Presentation
What: Chapter meeting and Presentation (2 CPE Hours)
When: Thursday, October 8, 2026
Hours: 11:30 am CDT – 1:30 pm CDT
Doors open at 11:00 am CDT
Agenda: Registration, Chapter Meeting, & Lunch Presentation
Location:
Ballroom at Tanglewood
5430 Westheimer Road
Houston, TX 77056
Home | The Ballroom at Tanglewood
ISSA South Texas Members: $20, includes 2 CPEs
ISSA Non-Member: $25, includes 2 CPEs
ISSA Walk-in Registrations: $30, Includes 2 CPEs
ISSA South Texas Student Admission: $15
Please Note:
***Advanced Registration closes Thursday, October 8, 2026 at 12:00 am Central***
Walk-in regstrations close Thursday, October 8, 2026 at 6:00 pm
Additional Note: Members, please verify your email address on file with ISSA. This is where all correspondence will be sent to members for CPE credit
Questions: Contact the ISSA South Texas Programs Director ([email protected])
Presentation Topic:
Agentic GRC: How AI Agents Are Changing the CISO's Playbook
GRC teams have spent years bolting automation onto fundamentally manual processes, automated reminders for manual evidence collection, dashboards built on manually updated spreadsheets. Agentic GRC represents a different model: AI agents that don't just flag work for humans, but actively execute it, answering vendor and customer security assessments, collecting evidence, managing and updating the risk register, drafting and maintaining policies, and generating reports on demand, in minutes rather than days, without waiting for a human to kick off each step.
This session explores what "agentic" actually means in a GRC context and why it matters now. We'll cover how autonomous agents can reduce the time spent answering and completing security questionnaires and assessments, continuously monitor and oversee the risk register, keep policy management current as regulations and internal standards shift, and generate board-ready and audit-ready reports on demand instead of through manual, multi-day compilation efforts, all while prioritizing remediation based on risk impact. The conversation will also address where agentic approaches still need human oversight, and how CISOs should think about validation, auditability, and trust when handing meaningful work to an AI agent.
For CISOs and GRC leaders, the payoff is fewer cycles spent on manual coordination and more time spent on judgment calls that actually require a human, faster audit readiness, real-time risk visibility, quick reporting generation, and a compliance program that scales without a proportional increase in headcount.
Key Takeaways for Attendees:
- What distinguishes "agentic" GRC from traditional automation, and how to tell the difference when evaluating vendors
- How AI agents are reducing the burden of assessment answering and completion
- How AI can help manage and oversee the risk register
- Using agents to draft, maintain, and update policy management as frameworks and regulations evolve
- Reporting generation: turning raw compliance data into board-ready output without manual assembly
- How to think about oversight, auditability, and trust when agents are executing compliance-critical tasks
- Framework consolidation: letting agents map one control across multiple frameworks and how to overcome increasing regulatory requirements
Speaker:
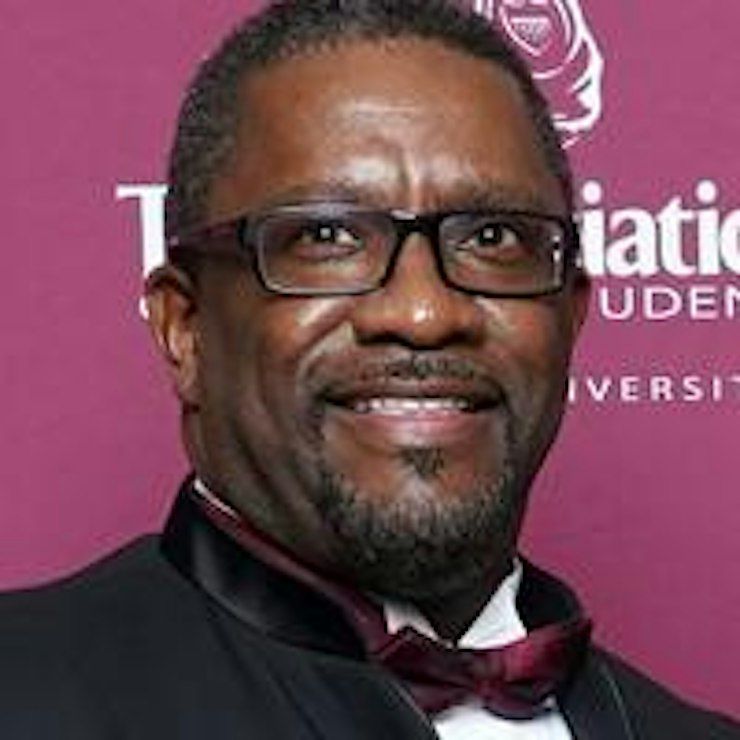
Llewellyn DerryFounder and President, Above Security
Mr. Llewellyn Derry is a seasoned IT risk management and cybersecurity executive with over 25 years of experience driving strategic security initiatives across Higher Education, Federal Government, and Global Enterprises. As an experienced Vice President, CISO, Managing Partner, and Board Advisor, he specializes in aligning governance, risk, and compliance strategies with business objectives, ensuring organizations can transform security challenges into market advantages. With expertise spanning cybersecurity leadership, IT governance, risk mitigation, and compliance management, Llewellyn has built a career on fortifying global enterprise digital infrastructures while enabling organizations to grow & scale securely both here in the United States and Overseas.
As the Founder and President of Above Security, he leads a GRC Management and Board Advisory Services firm serving organizations across the U.S., Canada, and the Caribbean. His team leverages over 300 man-years of combined cybersecurity expertise—spanning GRC Management, network and cloud security, risk assessments and penetration testing—to help clients proactively neutralize digital threats. This seasoned executive has played an integral role in assessing, strengthening, and enforcing IT risk postures and policies for organizations seeking to enhance the resilience of their IT infrastructure and their company at large.
Llewellyn’s global business acumen extends across industries, having held key leadership positions at Raytheon, Cisco Systems, AT&T, and Hitachi Systems Security. He has also taught Cyber Security courses at the Undergraduate and Graduate Level at the University of Dallas, Dallas Baptist University and Hacker University (in Israel).
Llewellyn holds an MBA in International Business from the University of Dallas, a Graduate Certificate in Corporate Finance from Southern Methodist University, and a Bachelor’s Degree in Economics and French from Texas A&M University. His professional certifications include C|CISO, CISSP, CISM and C|EH.
Where is it happening?
Event Location & Nearby Stays:
USD 17.85 to USD 535.38