Denver ISSA November 2026 Chapter Meeting (Lunch)

About this Event
Audit once, Apply to Many: Getting ahead of the new CCPA requirements
11:30pm -12:00pm - Networking & Lunch
12:00pm - 1:00pm - Presentation(CPE credits)
Abstract
California's updated CCPA regulations took effect in January 2026 and add a new requirement: an annual cybersecurity audit for businesses that meet the risk thresholds. The first certifications are due in April 2028 and cover your 2027 audit period, and many companies outside California are in scope without realizing it.
The good news is you probably already have most of what CCPA asks for. This session breaks down who's in scope, what the audit actually requires, and where the common gaps are. Then we'll walk through how to map CCPA onto your existing SOC 2, ISO 27001, and PCI controls so you can audit once and apply the results to many frameworks.
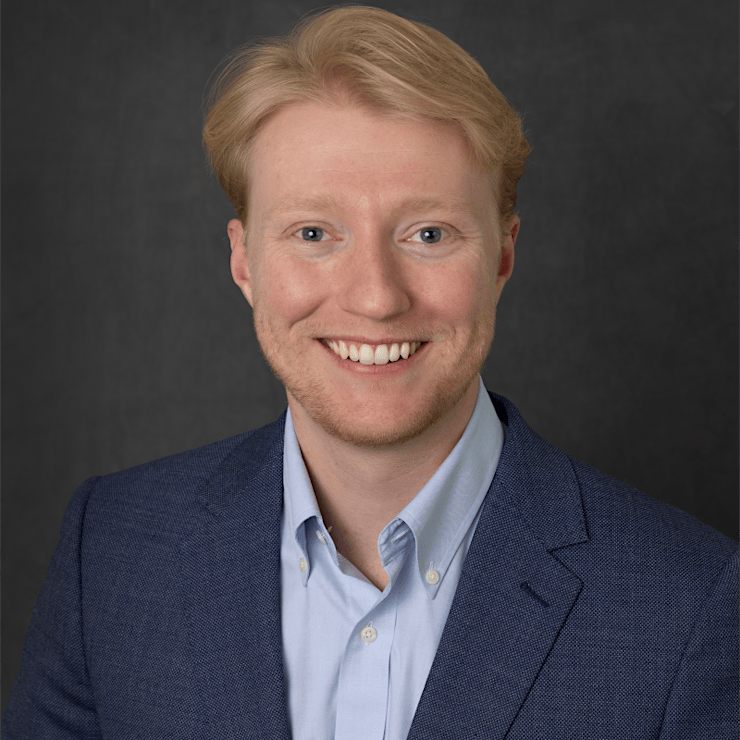
Speaker: ,Jackson Widener, Enterprise Audit Executive, KirkpatrickPrice, CPA
Jackson Widener is an Audit and Account Executive at KirkpatrickPrice, CPA, an audit and penetration testing firm, covering the Western US. He works with companies from early-stage startups to the Fortune 100 on SOC 2, ISO 27001, PCI, CMMC, and now CCPA. He helps security and compliance leaders cut audit fatigue by auditing once and applying that evidence across multiple frameworks. Outside of KirkpatrickPrice, Jackson is the founder of CyberMinds of Colorado, a networking group that brings security and compliance leaders together across the state to discuss mental wellness in cybersecurity. He's based in Colorado and also serves as Sponsorship Director for ISSA Denver.
ISSA would like to thank Black Kite, Varonis, Forescout, Armis, Rapid7, and Savvy our annual sponsors.
Where is it happening?
Event Location & Nearby Stays:
USD 0.00 to USD 28.52